

Amazon Connect
Hand Amazon Connect voice contacts to ElevenAgents through Amazon Connect’s native third-party AI agent (A2A) integration.
The Amazon Connect integration is in limited availability. Amazon Connect’s third-party AI agent support must be enabled for your AWS account, and the ElevenLabs transport is enabled per workspace. Contact your ElevenLabs representative before routing customer traffic.
Overview
The Amazon Connect integration connects an Amazon Connect contact flow directly to an agent in ElevenAgents over Amazon Connect’s third-party AI agent protocol, an extension of the open A2A protocol. Amazon Connect owns telephony, routing, and the queue; ElevenAgents owns the conversation. No SIP trunk, Twilio number, or middleware is required. AWS documents the feature under Agent-to-agent collaboration; this guide covers the ElevenLabs specifics and the AWS steps needed to reach an ElevenLabs agent.
The same flow serves inbound calls and outbound contacts started with StartOutboundVoiceContact.
When the ElevenLabs agent finishes, Amazon Connect continues your contact flow and branches on the
outcome it received.
How the integration works
- A contact flow reaches a Get customer input block that invokes an Amazon Lex V2 bot with the
AMAZON.QInConnectIntentintent. - Amazon Connect’s orchestration AI agent hands the conversation off immediately to the third-party application you registered for ElevenLabs.
- Amazon Connect opens a WebSocket to the ElevenLabs endpoint in the application’s
AccessUrl, authenticating with the API key stored in AWS Secrets Manager. - Amazon Connect signals that the caller’s channel is live, then Amazon Connect and ElevenLabs exchange 16-bit linear PCM audio as A2A messages. Amazon Connect proposes the sample rate and ElevenLabs adopts it, so no audio format changes are needed on the agent.
- When the agent ends the call, ElevenLabs finishes the session with a
Completeoutcome and the flow continues from the Lex block. AnEscalateoutcome, which routes the caller to a human queue, is supported on the wire and will be exposed through the transfer tool; see Transferring to a human.
Requirements
Before you begin, ensure you have:
- An Amazon Connect instance on the Connect Customer tier with third-party AI agent support enabled for the account and Region.
- An Amazon Q in Connect assistant associated with the instance.
- AWS permissions to create KMS keys, Secrets Manager secrets, AppIntegrations applications, Connect security profiles, Amazon Q in Connect AI agents, Lex V2 bots, and contact flows.
- An ElevenLabs workspace with the Amazon Connect transport enabled.
- An ElevenLabs agent and a dedicated API key.
- AWS CLI v2 and awscurl (
pip install awscurl) for the calls whose request shapes are not in released CLI versions yet.
Keep every AWS resource in the same account and Region as the Amazon Connect instance. The steps
below use the AWS CLI where it supports the call and awscurl (a SigV4-signed HTTP request) where
it does not. They follow AWS’s Set up collaboration with an external AI
agent and add the
ElevenLabs-specific values.
Configure ElevenLabs
Create or select an agent
Create the agent in ElevenAgents. Give it a first message if it should speak as soon as the hand-off completes; Amazon Connect plays nothing of its own during the session.
Enable End call
In Agent → Tools → System tools, enable End call so the agent can finish the session when
the caller’s request is resolved. Amazon Connect then continues your flow with the Complete
outcome.
Create a dedicated API key
Create an API key in the same workspace as the agent and scope it to ElevenAgents. You will store it in AWS Secrets Manager in the next section; do not paste it anywhere else.
Note the WebSocket URL
Amazon Connect connects to a URL that contains your agent ID:
If your ElevenLabs account is on an isolated residency environment, replace <region> with your
region code. See data residency for the available
regions.
Register the ElevenLabs application in AWS
Everything in this section is an API call. Set the values you will reuse once:
Create an Amazon Q in Connect assistant
Skip this step if the instance already has an assistant. Otherwise create one and associate it with the instance:
Record the assistant ID and ARN.
Store the API key
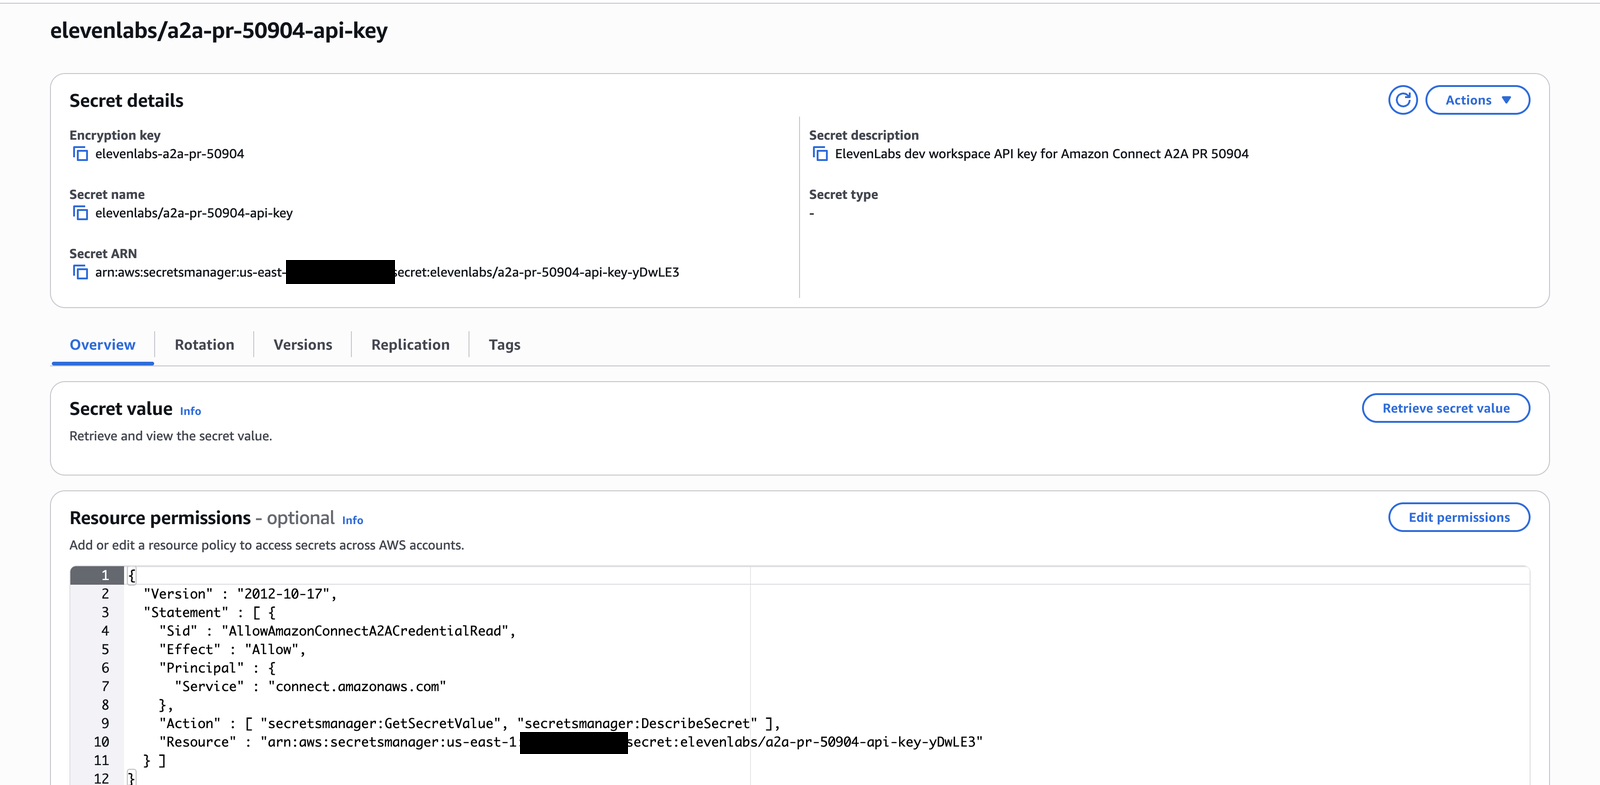
Amazon Connect reads the key from Secrets Manager with its own service principal, so the secret
must be encrypted with a customer-managed KMS key that grants connect.amazonaws.com decrypt
access. The default aws/secretsmanager key cannot be used.
Save the ElevenLabs API key in a file so that it never appears in your shell history, then create the key and the secret:
Grant Amazon Connect read access to the secret:
Create the third-party application
Register the ElevenLabs WebSocket URL as an AppIntegrations application of type A2A_SERVER.
AuthConfig is mandatory for this type.
The response contains the application Id and Arn; export them as APPLICATION_ID and
APPLICATION_ARN. The Amazon Connect console does not list A2A_SERVER applications, so verify
with the API:
Allow the application in a security profile
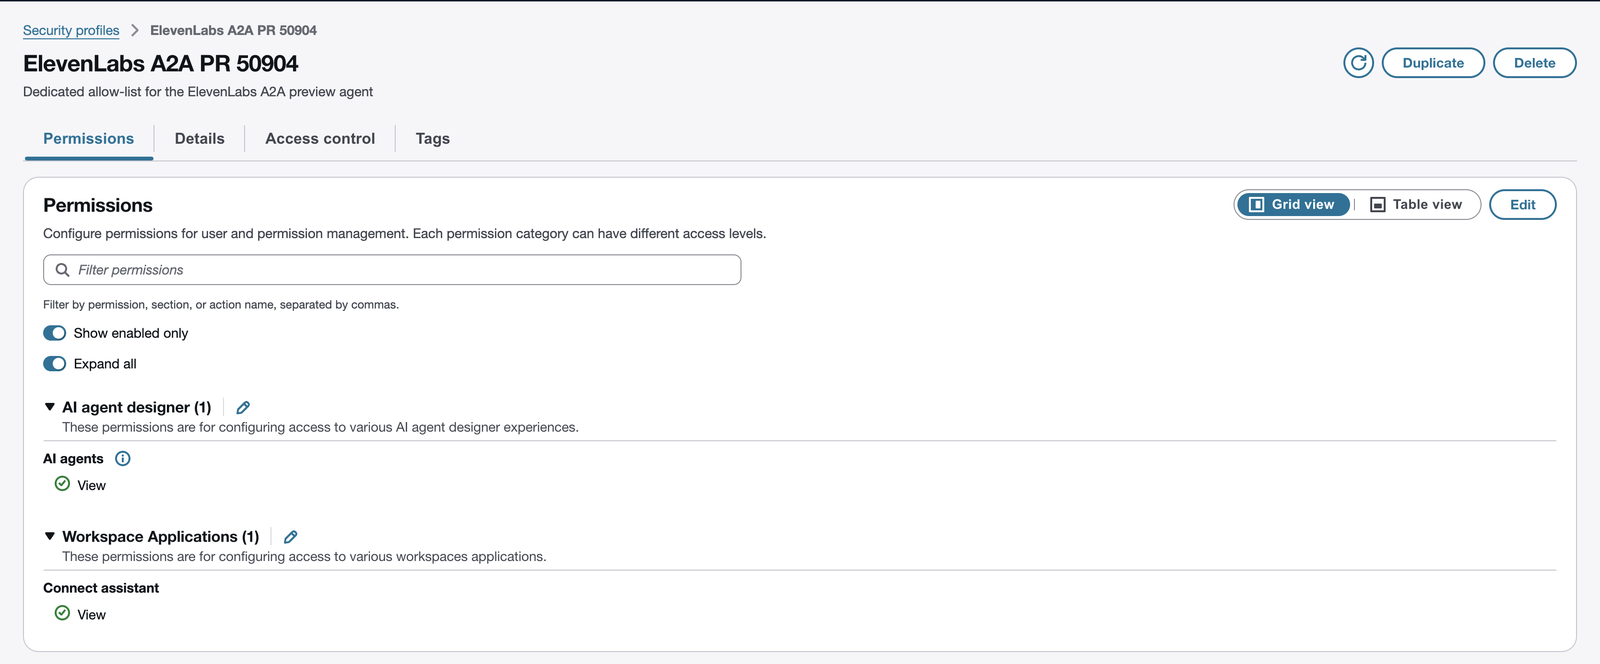
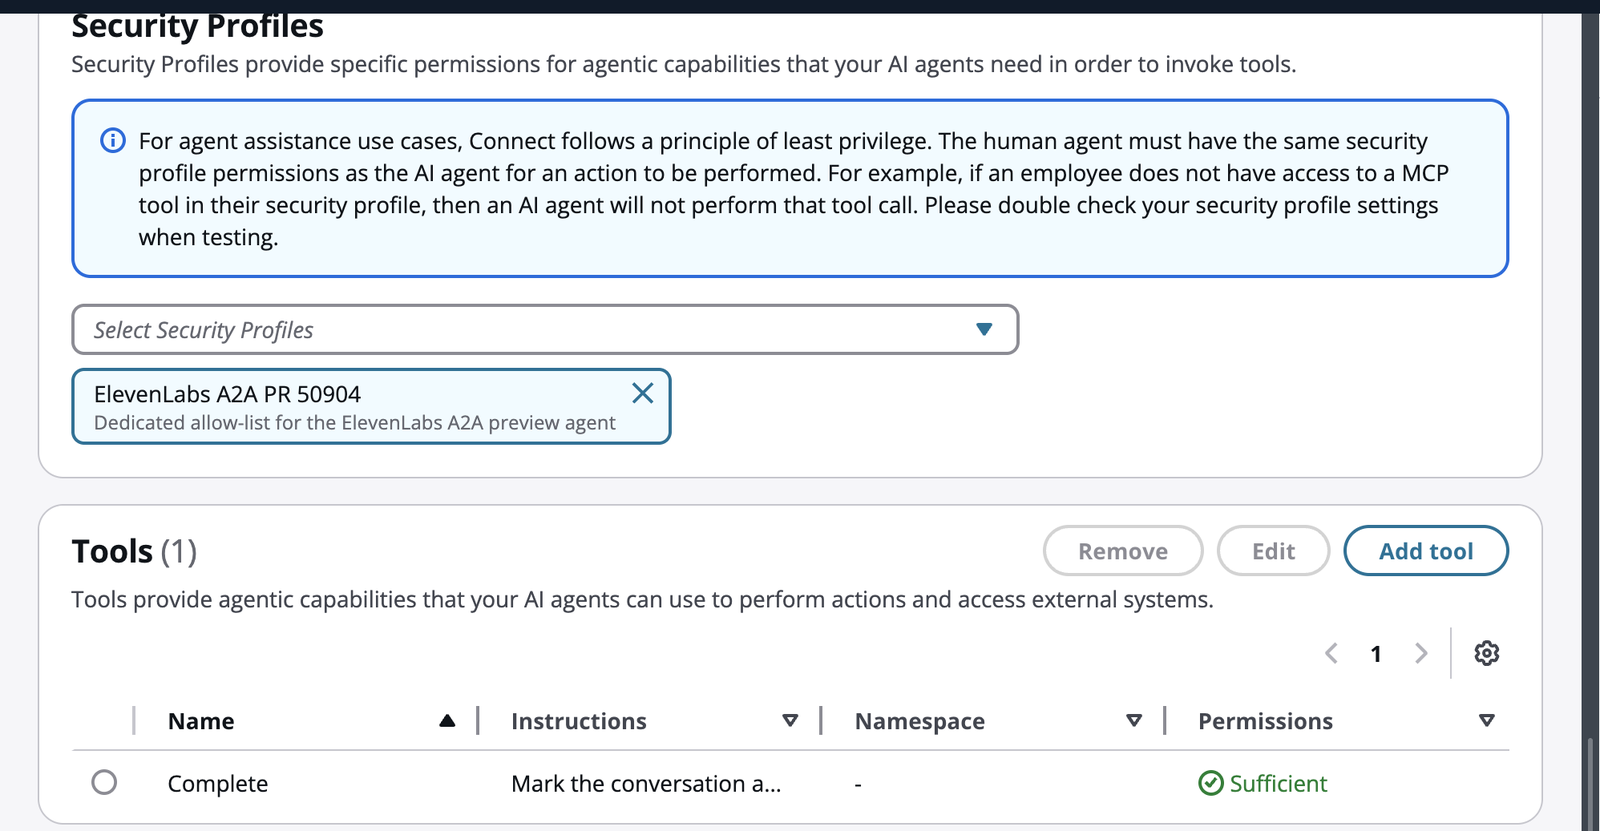
The security profile attached to the orchestration AI agent must list the application under its allowed AI agents, or the hand-off fails at runtime.
The admin website shows the profile and its permissions but not the allowed AI agents; those are only visible through the API.
Create and publish the orchestration AI agent
The orchestration agent hands every voice conversation to the application immediately, with audio
streaming enabled. Voice sessions require immediate hand-off; text streaming
(audioStreamingEnabled set to false) and delegateAgentConfiguration are not supported by
ElevenLabs.
Publishing returns a versioned ARN (<AI_AGENT_ARN>:1); the contact flow references it. Attach
the security profile to both the unversioned and the versioned agent:
Build the contact flow
Create the Lex bot
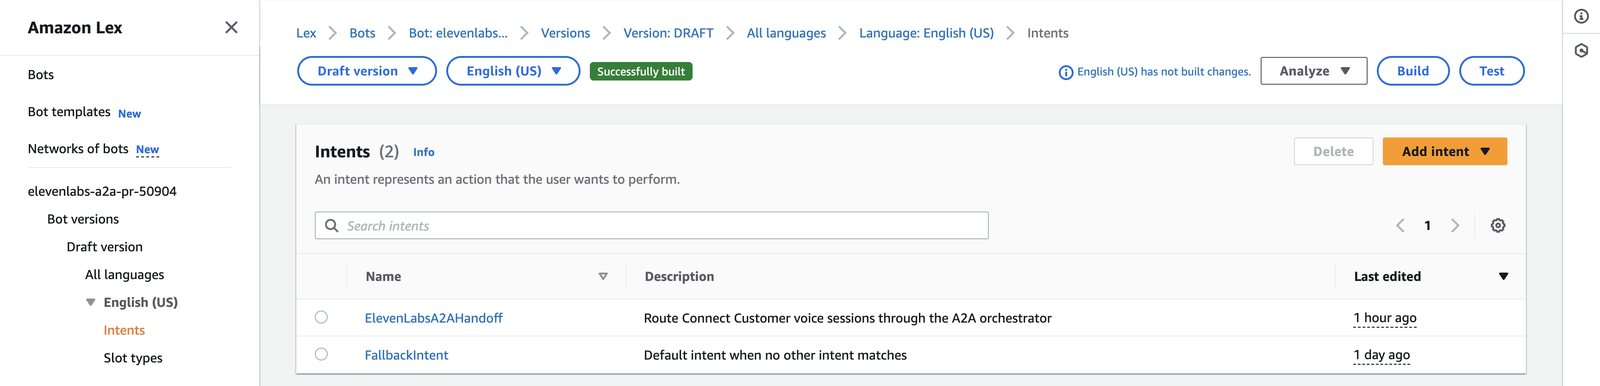
- Create a Lex V2 bot whose only intent is the built-in
AMAZON.QInConnectIntent, configured with your assistant ARN. Do not add other intents. - Enable speech-to-speech on the bot locale. Bidirectional audio streaming only works with Sonic speech-to-speech bots.
- Allow the bot’s IAM role to use the assistant. Without this the hand-off fails inside AWS with
HTTP 403before any request reaches ElevenLabs. Attach a policy like:
- Build the bot, create a version and an alias, and associate the alias with the instance:
Add the assistant and the Lex block
In the flow designer, add these blocks in order:
- Set logging behavior: enabled. The flow log is how you verify the hand-off below.
- Connect assistant: select your Amazon Q in Connect assistant.
- Get customer input: on the Amazon Lex tab choose Enter an ARN and paste the bot alias ARN. Leave the text-to-speech prompt as a single space so that Amazon Connect plays nothing before the hand-off. Under Session attributes, add two attributes set manually:
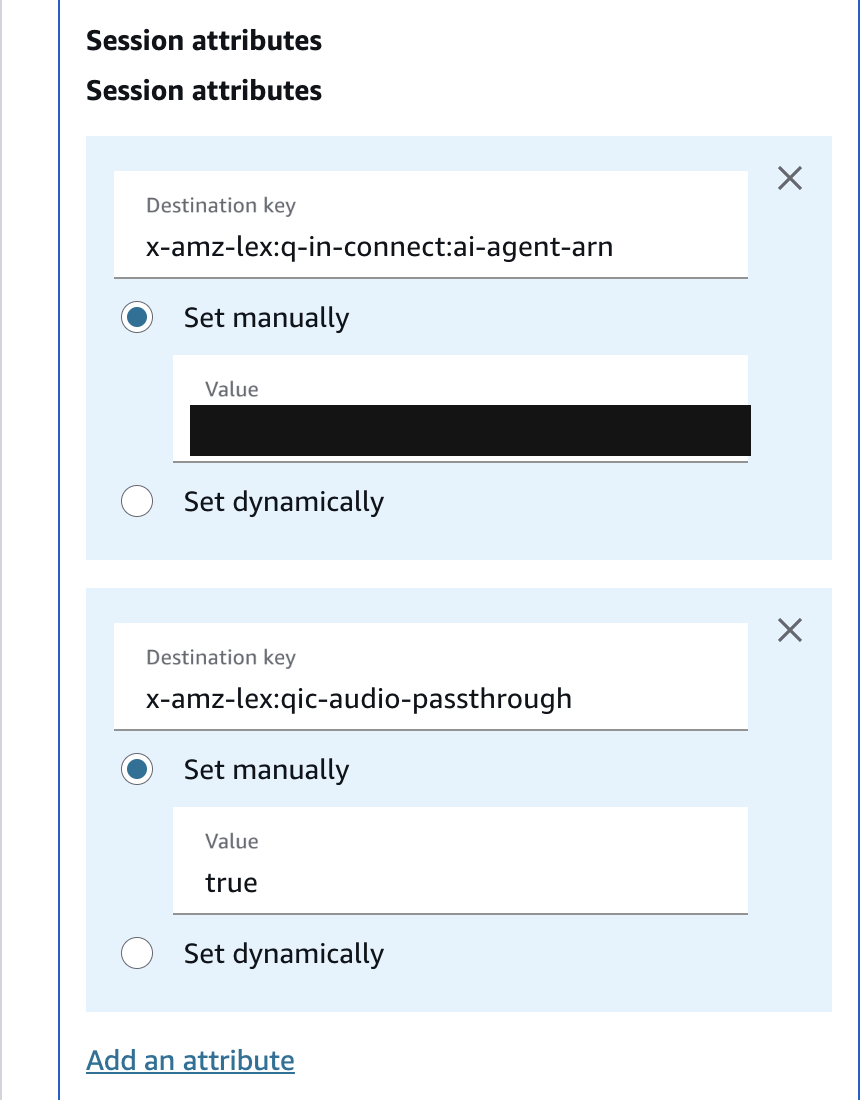
x-amz-lex:qic-audio-passthrough gates the third-party voice path during AWS’s prelaunch period.
AWS states the attribute is no longer needed once the feature is public; leaving it in place is
harmless.
Branch on the outcome
Amazon Connect surfaces the ElevenLabs outcome to the flow as the $.Lex.SessionAttributes.Tool
attribute. Add a Check contact attributes block after the Lex block, set Namespace to
Lex, Key to Session attributes, and Session Attribute Key to Tool, then add an
Equals condition per outcome:
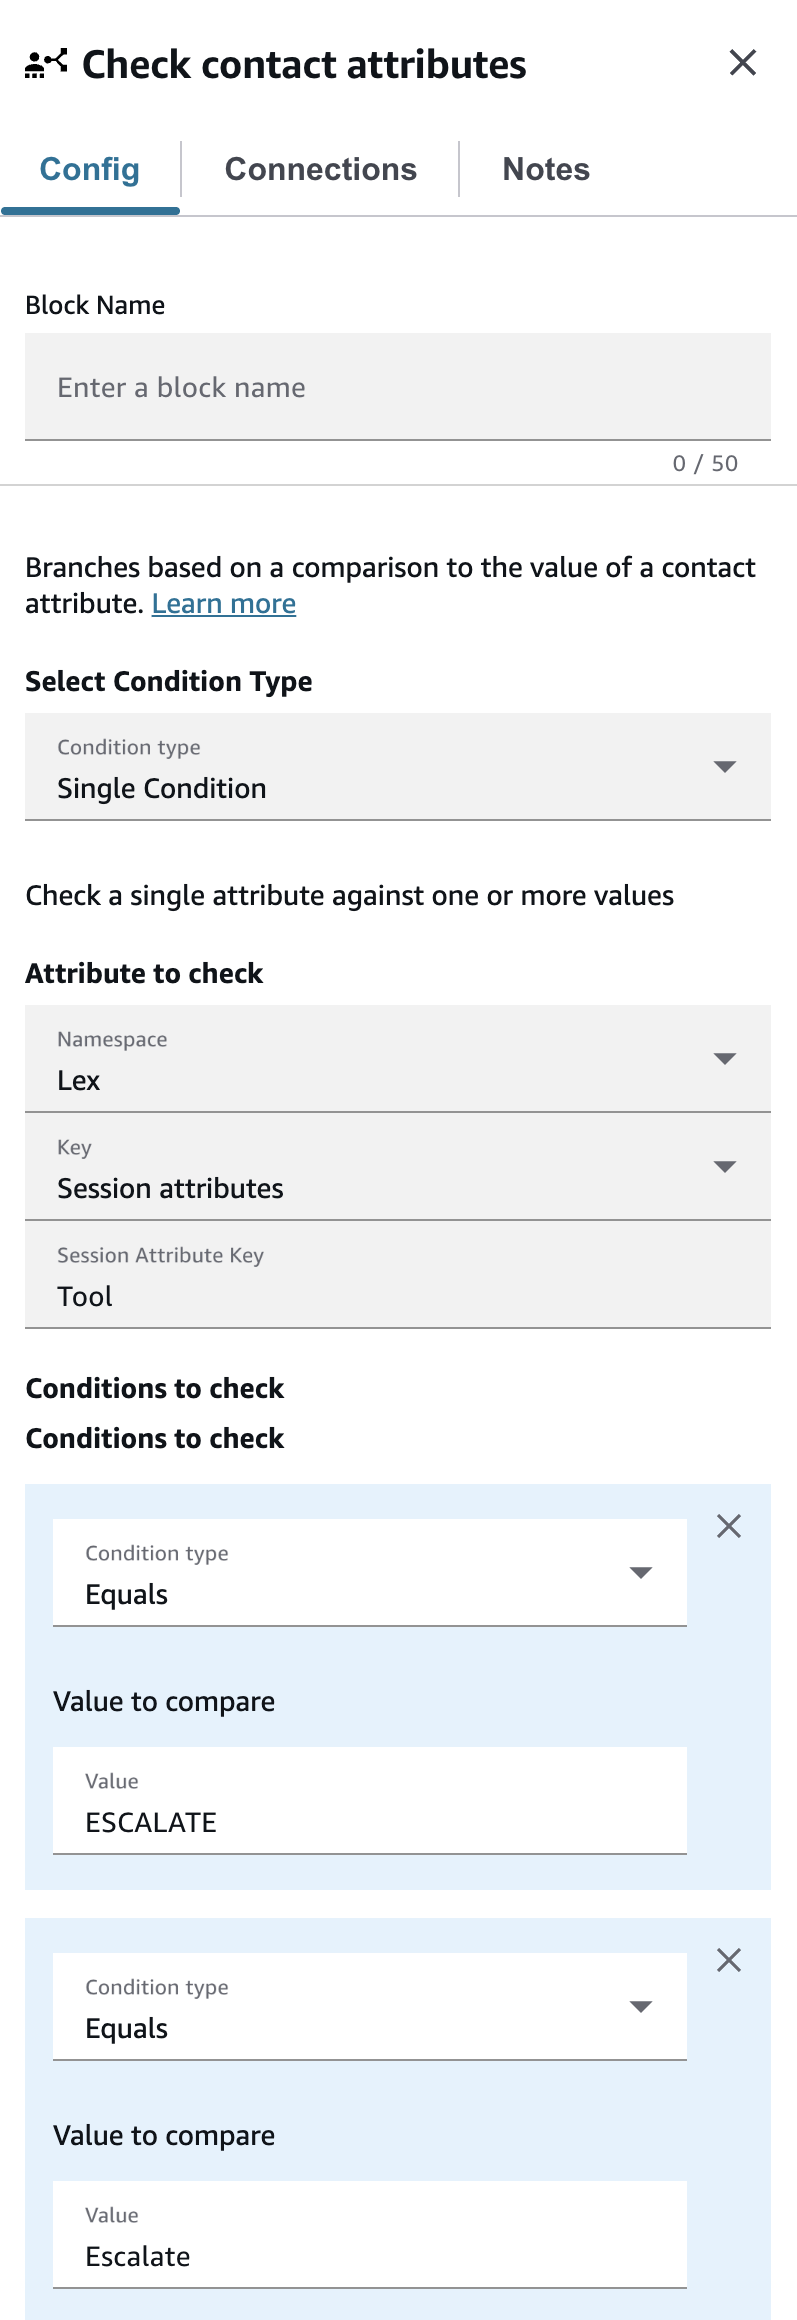
Amazon Connect writes these values in title case (Escalate, Complete), not as the upper-case
outcome type the agent sends. In an exported flow, the Lex block’s Default output is its
NoMatchingCondition transition; make sure it leads to the comparison block rather than an error
message.
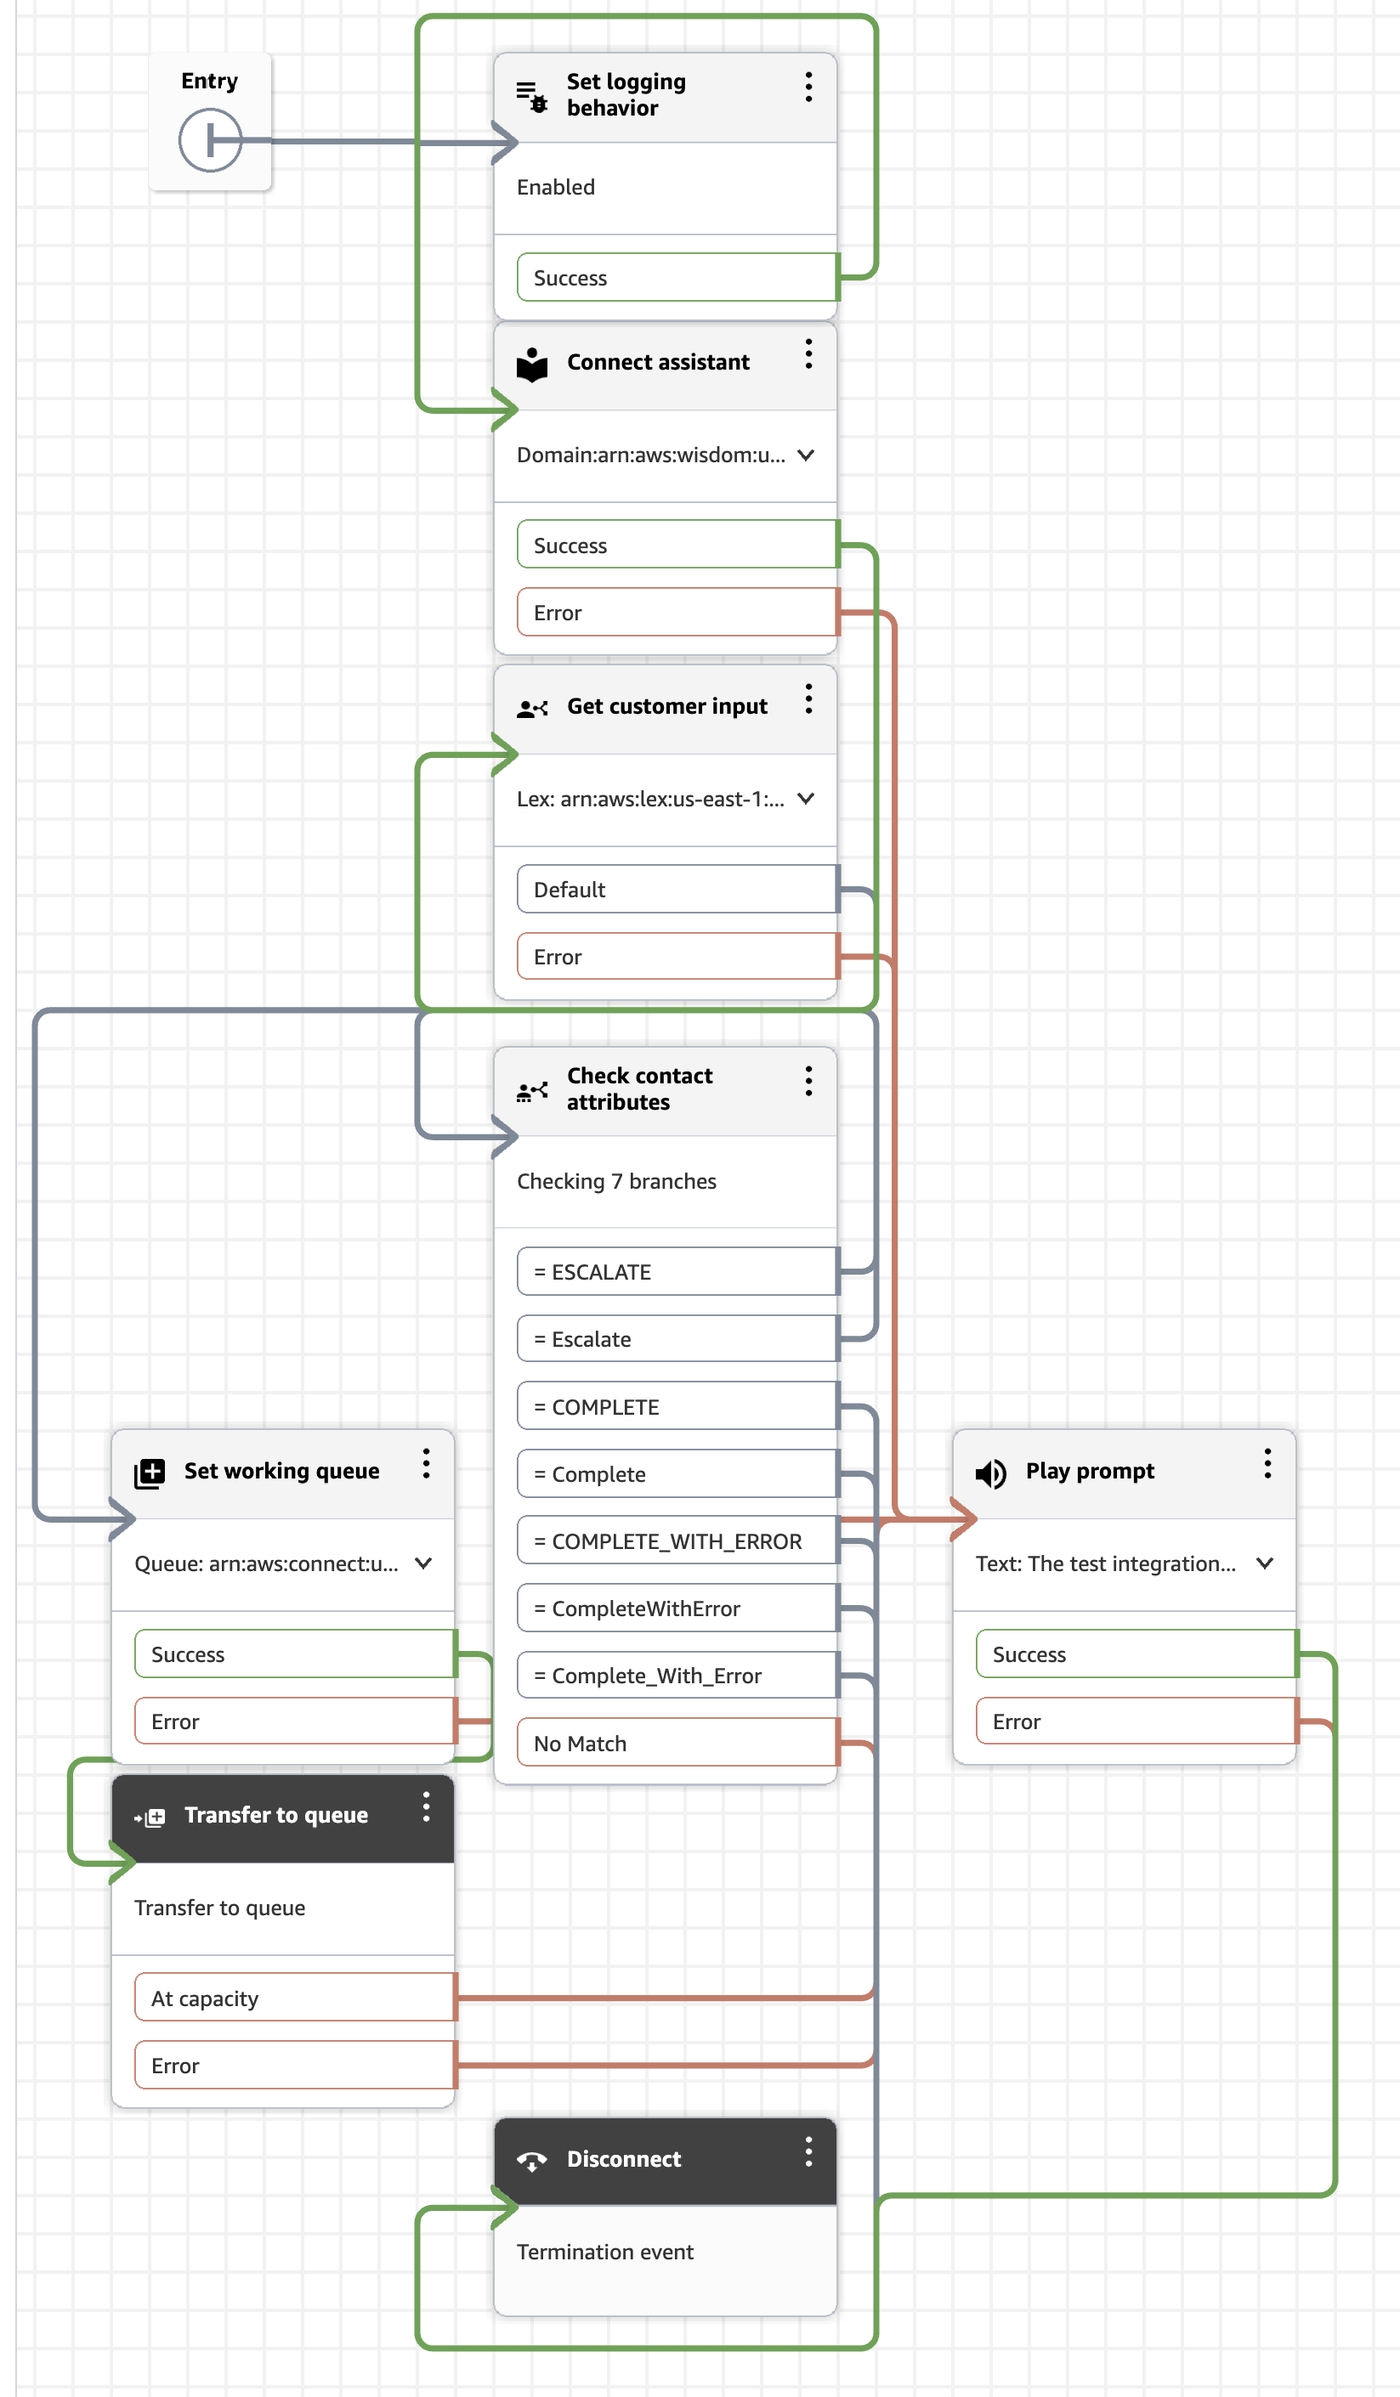
The flow above compares against both spellings of each outcome so it keeps working if the casing changes.
Test the integration
Place a call
Call the number. The agent’s first message plays a few seconds after the flow reaches the Lex
block; the hand-off inside AWS takes about three seconds before ElevenLabs is contacted. Have a
short conversation and say goodbye: the agent calls End call, the ElevenLabs session ends with
Complete, and your flow continues from the Lex block.
Dynamic variables
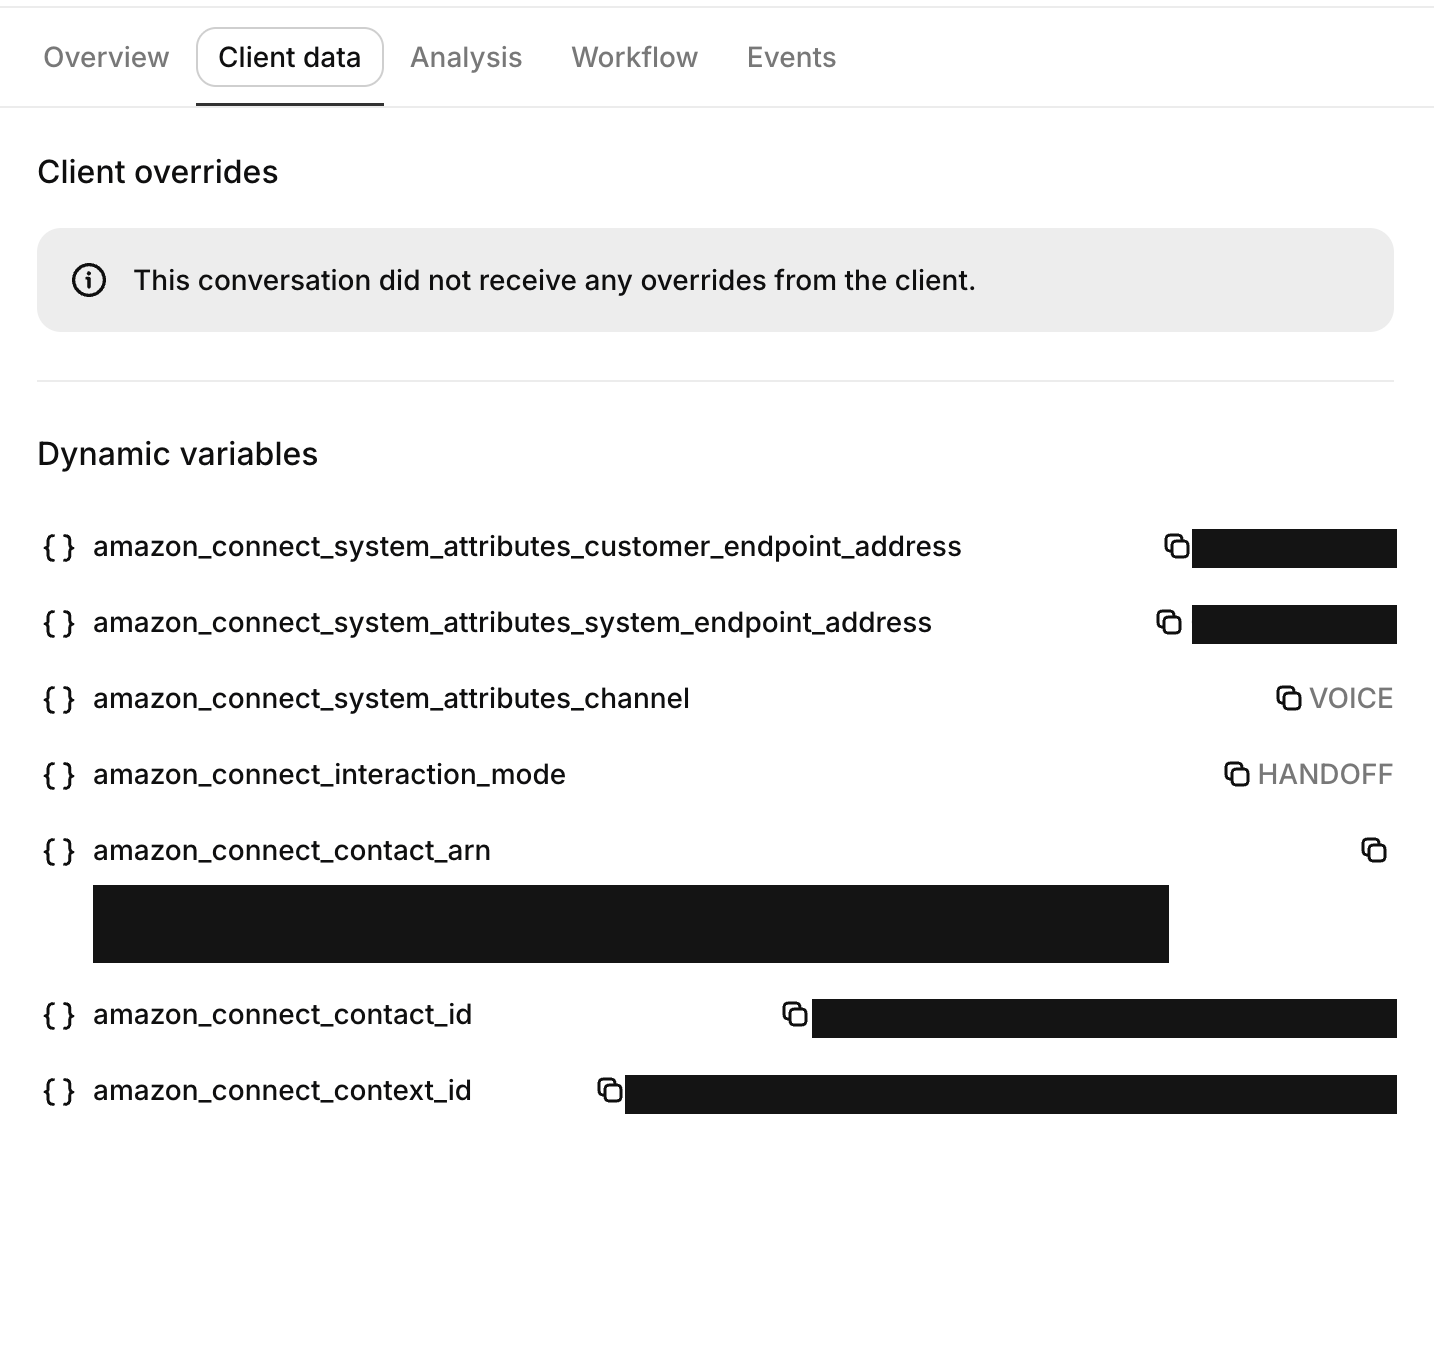
Amazon Connect sends the contact’s system attributes with every session. ElevenLabs exposes them, together with the session identifiers, as dynamic variables:
On Amazon Connect sessions system__caller_id is always the customer and system__called_number
is always the Amazon Connect number, for both inbound and outbound contacts.
Every other member of the contact context Amazon Connect sends is exposed the same way: nested
names are joined with underscores and converted to snake case under the amazon_connect_ prefix.
Custom contact attributes set in your flow with Set contact attributes are not part of the
context Amazon Connect currently sends, even when the AI agent’s security profile can view contact
attributes; if AWS starts including them, they will appear automatically under the same prefix. You
cannot choose which contact data Amazon Connect shares; AWS passes a fixed set of context.
To pass additional context, use the
conversation initiation webhook.
For Amazon Connect sessions the webhook is called before the agent speaks with caller_id set to
the customer’s number, called_number set to the Amazon Connect number, and call_id set to the
Amazon Connect contact ID, so a Lambda in your flow can store contact attributes keyed by contact ID
and the webhook can return them as dynamic variables and configuration overrides.
Transferring to a human
Amazon Connect routes a contact to a human queue when the ElevenLabs session ends with an
Escalate outcome, which your flow’s Escalate branch handles with Set working queue and
Transfer to queue. Any queue treatment, whisper flow, or agent selection is handled by Amazon
Connect.
The agent-side trigger for Escalate is being added to the Transfer to number tool as an
Amazon Connect transfer type, so that one tool covers human handoff on every provider. Until it
ships, ElevenLabs agents on Amazon Connect can end the call (Complete) but cannot escalate to a
human. Keep the Escalate branch in your flow; it starts working without further flow changes.
The End call tool produces a Complete outcome. Post-call analysis and the post-call webhook
run as usual after either outcome.
Only the outcome type and a reason string travel back to Amazon Connect. To hand routing data to
the flow, give the agent a webhook tool
that calls Amazon Connect’s UpdateContactAttributes API with amazon_connect_contact_id and the
values to store, and instruct the agent to call it before ending the call. The flow can then read
those attributes with a Check contact attributes block after the Lex block. The post-call
webhook fires after the flow has already continued, so it suits CRM updates rather than routing
decisions.
Traces
Amazon Connect requires external agents to send trace data for every collaboration. When Amazon Connect subscribes to tracing on the session, ElevenLabs sends an OpenTelemetry trace for each agent turn containing the caller’s transcript, the agent’s response, each tool call with its result, and per-span timing. Amazon Connect stores these traces with the contact; see AI agent traces for how to view them. Transcripts and tool results in these traces are subject to the same redaction settings as the rest of your contact data in Amazon Connect, so review your data-handling requirements before enabling the integration. Like post-call webhooks, traces are delivered to your own systems: agents in zero retention mode still send them, because zero retention governs what ElevenLabs stores, not what your Amazon Connect instance receives.
Audio
Amazon Connect proposes 16-bit mono linear PCM at 8, 16, or 24 kHz on each session and ElevenLabs adopts the proposal, so the agent’s configured audio formats are not used for Amazon Connect sessions. Caller barge-in is detected by ElevenLabs and reported to Amazon Connect so buffered playback is flushed immediately. Keypad input collected by Amazon Connect is delivered to the agent as DTMF digits. Amazon Connect’s own silence marker is ignored; use the agent’s turn timeout to re-prompt a quiet caller.
Limitations and unsupported features
- Client tools and the Play keypad touch tone system tool are not supported. Transfer to number does not yet support Amazon Connect; human handoff arrives as an Amazon Connect transfer type in that tool.
- Data collection results are not returned to the flow, and Amazon Connect decides which contact
data it shares. Use the conversation initiation webhook keyed by
amazon_connect_contact_idfor additional context, a webhook tool that callsUpdateContactAttributesfor routing data, and the post-call webhook for everything else. - Configuration overrides such as
system__override_first_messagecannot be passed from the flow. Return them from the conversation initiation webhook instead. - Voice sessions require immediate hand-off. The Amazon Connect chat channel, text streaming, and
behind-the-scenes (
delegateAgentConfiguration) collaboration are not supported yet. - Traces sent to Amazon Connect cover the caller’s transcript, the agent’s responses, tool calls with their results, and timing. Tool call parameters are not included.
- Amazon Connect’s third-party agent support is only available where AWS has enabled it and may incur additional AWS charges.
Troubleshooting
The flow fails with 'A2A WebSocket upgrade ... failed (HTTP 403)'
- The error is raised inside AWS before any request reaches ElevenLabs. Check CloudTrail for
AccessDeniedonwisdom:SendMessagefrom the Lex service role: the role attached to the bot needswisdom:CreateSession,wisdom:GetAssistant,wisdom:SendMessage, andwisdom:GetNextMessageon the assistant and its sessions. - Confirm the security profile allows the application and is associated with the published orchestration agent version referenced by the flow.
- Confirm the secret’s KMS key and resource policy grant
connect.amazonaws.comaccess.
The flow fails with 'the hand-off to the target agent could not be completed'
- Amazon Connect gives the WebSocket connection roughly 20 seconds to come up. Confirm the
AccessUrlis reachable from AWS:wss://, the right agent ID, no network allow-list in the way. - If you proxy the connection through your own infrastructure, keep that proxy warm. A cold serverless instance can take longer than the hand-off window, and Amazon Connect gives up before ElevenLabs ever sees the request.
The Lex block takes its Error branch and the caller hears nothing
- Confirm both session attributes are set on the Get customer input block:
x-amz-lex:q-in-connect:ai-agent-arnwith the published, versioned agent ARN andx-amz-lex:qic-audio-passthroughset totrue. - Confirm the security profile that allows the application is attached to that agent version.
- Read the block’s entry in the flow log; it carries the error Amazon Connect encountered.
The session ends immediately after connecting
- Confirm the
AccessUrluseswss://, contains the correct agent ID, and points at the region your workspace lives in. - Confirm the API key is active, belongs to the agent’s workspace, and has no IP restrictions.
- Confirm the Amazon Connect transport is enabled for your workspace.
The caller hears the flow's error prompt after the agent finishes
In the Lex block, make sure the Default output leads to the block that compares
$.Lex.SessionAttributes.Tool, and compare against the title-case values Escalate and
Complete.
The agent never speaks and the session ends after a few seconds
Confirm the collaborator is configured with audioStreamingEnabled set to true. With text
streaming, Amazon Connect sends text turns and expects text responses, which ElevenLabs does not
support; the ElevenLabs logs show INIT_SESSION carries no audio configuration.
Dynamic variables are missing
Amazon Connect provides the contact system attributes and identifiers listed above. Custom contact attributes set in the flow do not reach the agent; pass them through the conversation initiation webhook instead. If the agent’s first message or prompt references a variable that is never provided, the session fails at startup.